Open to cybersecurity roles

Securing networks,
applications and data.

I'm Yasir Hassan, a Computer Engineering student at Bahria University, Islamabad. After a cybersecurity internship at Safe City Islamabad, I focus on vulnerability assessment, web application security and threat intelligence, and I build software with security designed in from the start.

NowFinal year of B.E. Computer Engineering · building VigiLense, my AI surveillance FYP

Portrait of Yasir Hassan
Yasir HassanIslamabad, Pakistan Open to work

Selected work

All repositories ↗
Final Year Project2026 · In progress

VigiLense →

AI surveillance and incident response. Watches multiple camera feeds, detects people, weapons, fire and smoke, ranks incidents by priority, and logs evidence-backed alerts on a live dashboard. I lead the detection work in a team of three.

  • 0.78 mAP50 on my fire & smoke model
  • 3+ camera feeds with auto switching
  • End-to-end video → alert → dashboard
  • Python
  • PyTorch
  • YOLO
  • FastAPI
  • SQLite
Desktop application2026

Milkiyat →

Secure blockchain land records. Each approved record is a block signed with RSA-2048 on a SHA-256 hash chain, with owner data encrypted using AES-256-GCM, TOTP two-factor login, role-based access and tamper detection.

  • Python
  • Cryptography
  • Blockchain
  • RBAC
Web platform2026

Dastarkhwan →

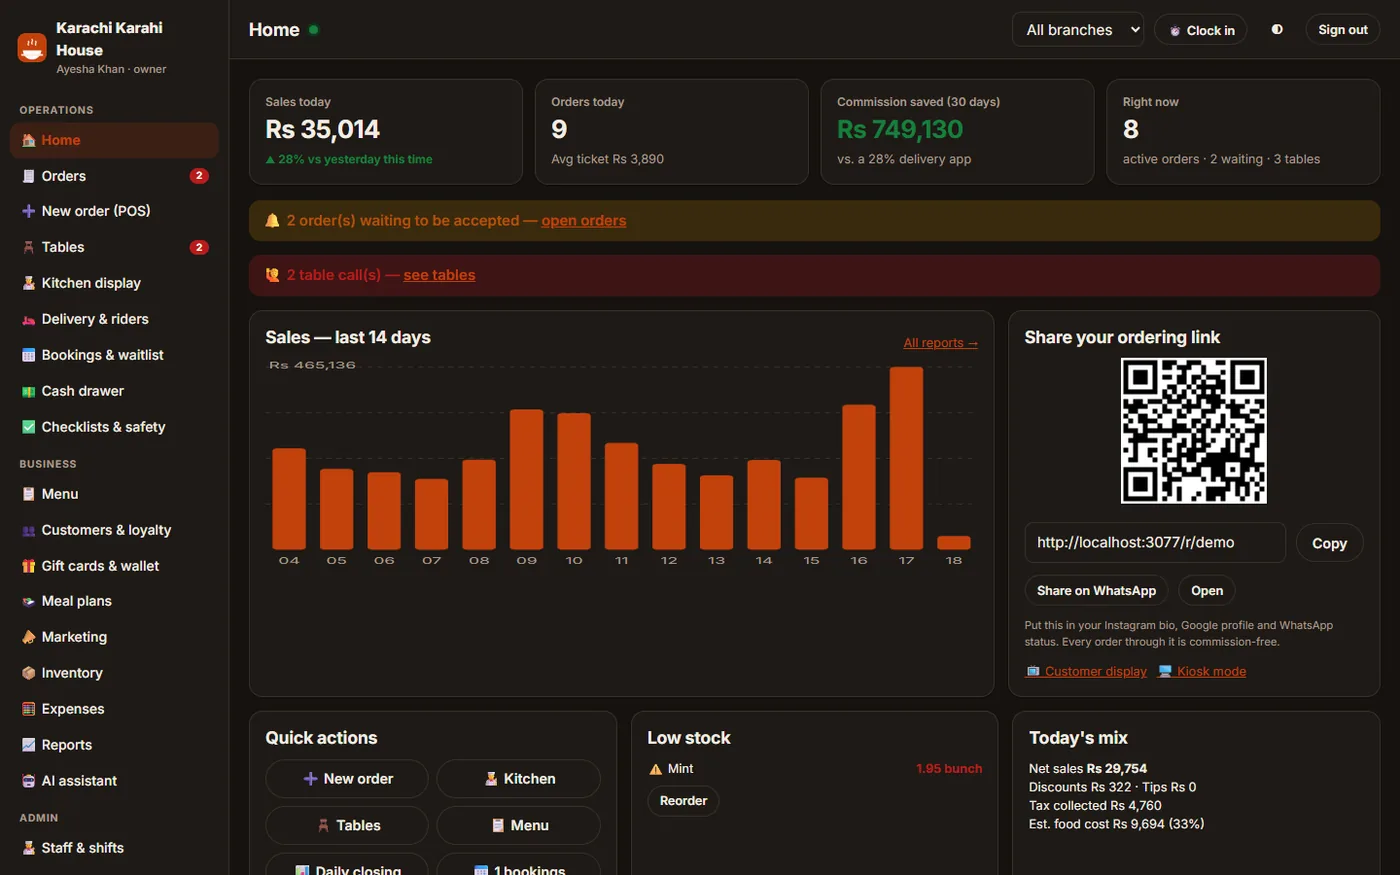
Commission-free ordering and management for restaurants: ordering links, QR table menus, kitchen display, POS, rider app, reports, inventory and tax invoices.

  • Node.js
  • JavaScript
  • Realtime
Academic project2026

HRMS ↗

Role-based HR system in Java Swing with six dashboards, SHA-256 password hashing, access control and a full audit log on SQL Server.

  • Java
  • JDBC
  • SQL Server
Academic project2025

Enterprise Network ↗

Three-layer campus network with VLAN segmentation, inter-VLAN routing, NAT, DHCP, ACLs, port security, SSH management and QoS.

  • Cisco
  • VLAN
  • ACL
  • QoS

Experience

Jun 2026 — Sep 2026

Cybersecurity Intern · Safe City Islamabad

  • Assisted with vulnerability assessment activities and security testing.
  • Tested web applications for security flaws using Burp Suite.
  • Conducted cyber threat intelligence (CTI) research on threats and incidents from open sources.
  • Gained hands-on experience with defensive security operations and assessment methodology.
2023 — 2027

B.E. Computer Engineering · Bahria University, Islamabad

Coursework in Network Security, Computer Networks, Data Structures, Embedded Systems, Microcontrollers & IoT, and AI & Machine Learning.

How I work

A structured approach to security assessment, guided by the OWASP Testing Guide and NIST practice.

  1. 01

    Scope & recon

    Agree what's in scope, then map the attack surface: hosts, services, endpoints and exposed data.

    • Nmap
    • OSINT
  2. 02

    Assess

    Test against the OWASP Top 10 with tooling and manual checks, so findings are real, not scanner noise.

    • Burp Suite
    • Wireshark
  3. 03

    Validate & prioritise

    Confirm impact, rate severity and rank issues by real business risk rather than by count.

    • CVSS
    • Threat modelling
  4. 04

    Report & remediate

    Write clear findings with evidence and fix steps developers can act on, then retest the fixes.

    • Reporting
    • Retesting

When I build software, I apply the same thinking from the start: least privilege, defence in depth and tamper evidence, as in Milkiyat and Dastarkhwan.

Skills

Everything here is backed by real work: each row links to where I used it.

Application Security
  • Vulnerability Assessment
  • Web App Testing
  • OWASP Top 10
  • Ethical Hacking
  • Security Testing

Used in Safe City internship

Threat Intel & Defense
  • Cyber Threat Intelligence
  • OSINT
  • Incident Response
  • Digital Forensics
  • Audit Logging
  • Tamper Detection

Used in Safe City internship, Milkiyat

Applied Cryptography
  • AES-256-GCM
  • RSA-PSS Signatures
  • SHA-256 Hash Chains
  • PBKDF2
  • scrypt
  • HMAC Tokens
  • TOTP (RFC 6238)

Used in Milkiyat, Dastarkhwan, HRMS

Secure Development
  • RBAC
  • Separation of Duties
  • Input Validation (Zod)
  • Parameterized SQL
  • Rate Limiting
  • Content Security Policy
  • Secure Cookies
  • Security Headers

Used in Dastarkhwan, Milkiyat, HRMS, this website

Network Security
  • VLAN Segmentation
  • Inter-VLAN Routing
  • ACLs
  • NAT
  • DHCP
  • Port Security
  • SSH Hardening
  • QoS
  • OSPF
  • RIP
  • TCP/IP
  • DNS
  • Subnetting
  • 3-Layer Network Design

Used in Enterprise Network

AI & Computer Vision
  • PyTorch
  • Ultralytics YOLO
  • OpenCV
  • Object Detection
  • Model Training & Evaluation
  • Real-time Video Pipelines
  • LLM Integration (Claude API)

Used in VigiLense, Dastarkhwan

Backend & Data
  • Node.js
  • FastAPI
  • REST APIs
  • Server-Sent Events
  • Multithreading
  • SQLite
  • SQL Server
  • JDBC
  • Schema Design
  • Automated Testing

Used in Dastarkhwan, VigiLense, HRMS

Frontend & Apps
  • HTML
  • CSS
  • JavaScript
  • Progressive Web Apps
  • Responsive Design
  • Java Swing
  • Tkinter

Used in Dastarkhwan, HRMS, Milkiyat

Languages
  • Python
  • Java
  • JavaScript
  • SQL
  • C
  • C++
Tools & Platforms
  • Burp Suite
  • Wireshark
  • Nmap
  • Linux
  • TryHackMe
  • Cisco Packet Tracer
  • Git & GitHub
  • Google Colab
  • VS Code

Writeups

All writeups →

Let's talk.

I'm open to cybersecurity internships and entry-level roles in security operations, vulnerability assessment and application security. I usually reply within a day.